As applications become central to business operations, application security has moved beyond the development team and into enterprise risk management. Cloud platforms, APIs, third-party dependencies, and continuous software releases have created a larger and more complex security environment.
An application security manager helps organizations manage this environment by combining security strategy, software development, governance, and risk management. The role is responsible for establishing security practices that protect applications throughout their lifecycle while supporting business and technology objectives.
The Strategic Importance of Application Security
Applications are now a major part of the enterprise attack surface. Customer portals, mobile applications, APIs, internal platforms, and cloud-based services often handle sensitive information and critical business processes.
Modern development practices add further complexity. Continuous deployment, microservices, open-source dependencies, third-party integrations, and cloud infrastructure can introduce new security risks with every change.
This makes application security management an ongoing business responsibility rather than a final security check before deployment.
A mature program needs to answer several practical questions:
- Which applications are most important to the business?
- Where are the major security exposures?
- Which vulnerabilities require immediate attention?
- Are security controls being applied consistently?
- How quickly are important findings being remediated?
- Are development teams receiving useful security guidance?
The application security manager helps establish the processes and governance needed to answer these questions consistently.
What Is an Application Security Manager?
An application security manager is a cybersecurity professional responsible for leading or coordinating the security of an organization’s applications.
The role combines technical knowledge with management, governance, and risk assessment. Depending on the organization, the manager may lead an application security team, oversee security testing programs, define security standards, or work directly with engineering and development leadership.
The position generally focuses on ensuring that security is considered from application design through production and ongoing maintenance.
Core responsibilities commonly include:
- Developing application security strategy
- Establishing secure development standards
- Overseeing application security testing
- Managing vulnerability remediation
- Assessing application security risks
- Supporting regulatory and audit requirements
- Managing third-party and software supply chain risks
- Monitoring application security performance
- Working with development and engineering teams
- Reporting security risks to senior leadership
The role is therefore broader than vulnerability scanning or penetration testing. It involves building a security program that can operate consistently across an organization’s application portfolio.
Core Responsibilities of an Application Security Manager
Defining the Application Security Strategy
An application security manager typically helps define the organization’s overall application security strategy.
The strategy establishes how applications should be designed, developed, tested, deployed, and maintained securely. It may include secure coding standards, security testing requirements, vulnerability management procedures, risk acceptance processes, and escalation rules.
At enterprise scale, standardization is important because different development teams may otherwise follow completely different security practices.
The strategy also needs to account for business priorities. Security requirements should be strong enough to reduce meaningful risk without unnecessarily disrupting software delivery.
Embedding Security Into the SDLC
Application security is more effective when it is integrated throughout the software development lifecycle.
An application security manager may establish security activities at each stage, including threat modelling during design, secure coding practices during development, automated security testing in CI/CD pipelines, validation before release, and monitoring after deployment.
This approach is closely associated with DevSecOps, where security becomes part of normal development and delivery processes.
The objective is to identify security weaknesses earlier, when they are generally easier to understand and address.
Overseeing Application Security Testing
Security testing is another major responsibility.
Depending on application requirements and risk, an application security program may include:
- Static Application Security Testing (SAST)
- Dynamic Application Security Testing (DAST)
- Software Composition Analysis (SCA)
- Interactive Application Security Testing (IAST)
- API security testing
- Manual code reviews
- Penetration testing
- Configuration assessments
The application security manager does not simply need to ensure that tools are being used. The role also involves determining whether testing provides sufficient coverage and whether findings are being handled according to their actual risk.
Vulnerability Management and Risk Prioritization
Large application environments can produce thousands of security findings. Treating every finding as equally urgent can overwhelm development teams and reduce the effectiveness of the security program.
The application security manager helps establish a risk-based prioritization process.
Technical severity is one consideration, but other factors can include application exposure, data sensitivity, exploitability, business importance, threat activity, and existing security controls.
This allows remediation resources to be directed toward issues that represent meaningful business risk.
Application Security Management
Application security management is the broader discipline through which organizations plan, operate, and improve application security.
It includes the people, processes, policies, technologies, and governance mechanisms used to protect software throughout its lifecycle.
A structured application security management program normally covers:
- Security requirements
- Secure architecture
- Development practices
- Security testing
- Vulnerability management
- Application monitoring
- Access controls
- Dependency management
- Incident response
- Risk management
- Governance and compliance
The application security manager often acts as the person who brings these activities together.
Application Security Posture Management
Application security posture management focuses on understanding the overall security condition of applications and their supporting environments.
Application security information is often spread across many different tools. SAST may identify code vulnerabilities, SCA may identify vulnerable dependencies, DAST may identify weaknesses in running applications, while cloud and infrastructure tools may identify configuration issues.
Looking at each result separately can make it difficult to understand the actual security posture.
Application security posture management helps bring these findings together so teams can gain broader visibility, correlate related issues, prioritize risks, and track remediation.
This lifecycle-oriented approach is different from a single security test because it considers application security across development, deployment, and production.
Key Areas of Application Security Posture
A useful application security posture can include visibility into:
- Application inventory
- Application ownership
- APIs and external interfaces
- Security vulnerabilities
- Open-source dependencies
- Cloud resources
- Security testing coverage
- Configuration weaknesses
- Remediation status
- Security exceptions
- Application criticality
The objective is to give security and engineering leaders a more complete picture of where security risks exist and how they are being managed.
Application Security Risk Management
Application security risk management focuses on identifying, evaluating, prioritizing, treating, and monitoring risks associated with applications.
It is broader than simply identifying vulnerabilities.
A vulnerability is a technical weakness. Risk considers the likelihood that the weakness could lead to harm and the potential consequences if it were exploited.
For example, a vulnerability affecting a public-facing application that processes sensitive customer data may require a different response from the same vulnerability in an isolated development environment.
Risk management brings this context into security decisions.
Identifying Application Risks
Risk identification can involve vulnerabilities, insecure configurations, exposed APIs, weak authentication, outdated dependencies, poor access controls, and architectural weaknesses.
Threat modelling can also identify potential attack paths before an application reaches production.
Assessing and Prioritizing Risk
Once a risk is identified, security teams can assess factors such as:
- Exploitability
- Internet exposure
- Application criticality
- Data sensitivity
- Potential business impact
- Existing security controls
- Threat activity
This information helps determine whether a finding requires immediate remediation, additional mitigation, or treatment through a normal development cycle.
Treating Application Security Risk
Risk treatment can involve fixing the underlying issue, applying a compensating control, changing a configuration, reducing exposure, transferring the risk, or formally accepting it.
Accepted risks should have clear ownership and should be reviewed periodically because application environments and threat conditions change.
Governance and Compliance Responsibilities
Application security also has a governance dimension.
Organizations may operate under data protection laws, industry standards, contractual security requirements, and internal policies. The application security manager helps ensure that security practices support these obligations.
This can include maintaining evidence such as:
- Security testing results
- Vulnerability records
- Remediation information
- Security policies
- Risk exceptions
- Application inventories
- Third-party security assessments
The goal is not simply to prepare for an audit. Good governance creates a repeatable structure for managing security across applications.
Third-Party and Software Supply Chain Risk
Modern applications rarely consist entirely of internally developed code.
Organizations commonly rely on open-source packages, commercial software, cloud services, APIs, SaaS platforms, and external development partners.
These dependencies create additional security considerations.
An application security manager may establish processes for dependency monitoring, supplier security reviews, open-source governance, software composition analysis, and security requirements for external development partners.
Managing software supply chain risk is particularly important because a vulnerability in a widely used component can potentially affect many applications at the same time.
Operating Model for Application Security
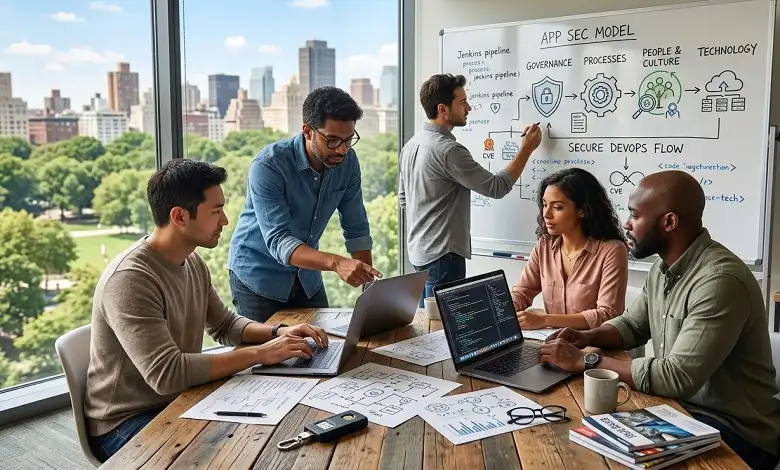
Large organizations often use a combination of centralized governance and distributed execution.
A central application security team can define standards, approve security tools, establish policies, and maintain common processes. Development teams then apply those requirements within their own applications.
Security champions can provide another layer of support by bringing application security knowledge into individual engineering teams.
This model allows organizations to maintain consistent security expectations without requiring every development decision to pass through a central security team.
The application security manager typically coordinates this model and works with engineering leaders, architects, cloud teams, compliance functions, and enterprise risk teams. The sample enterprise model similarly emphasizes centralized strategy with execution distributed across development teams.
Measuring Application Security Performance
Application security programs need meaningful measurements to determine whether security is improving.
Activity metrics alone can be misleading. For example, running more scans does not necessarily mean that application risk has decreased.
A stronger measurement approach focuses on outcomes.
| Metric Area | Example Measurement | Purpose |
| Risk exposure | Critical vulnerabilities by application | Helps prioritize remediation |
| Remediation | Average time to resolve high-risk findings | Measures response effectiveness |
| Security coverage | Percentage of applications receiving required testing | Shows program coverage |
| Development | Security defects identified before production | Indicates early security integration |
| Resilience | Application security incidents | Tracks security outcomes |
Executive reporting should translate technical information into business-relevant risk rather than overwhelming leadership with raw vulnerability counts.
Skills Required for an Application Security Manager
The role requires a combination of technical depth, business awareness, and leadership.
Technical Knowledge
An application security manager should understand application architecture, secure coding, authentication, authorization, APIs, cloud environments, software dependencies, security testing, and vulnerability management.
The level of hands-on technical knowledge varies by organization, but the manager needs enough understanding to evaluate security decisions and communicate effectively with engineers.
Risk and Governance
Technical knowledge alone is not enough at the enterprise level.
The role also requires an understanding of risk assessment, security governance, compliance, policies, and business priorities.
An application security manager must be able to explain why a technical issue matters from a business perspective.
Leadership and Communication
Application security affects many teams, so the manager needs to influence people outside the security function.
This includes working with development leaders, architects, product teams, operations, legal, compliance, and senior executives.
Strong communication helps turn security requirements into practical development practices rather than simply creating additional controls.
Common Challenges in Application Security Management
Scaling Across Multiple Teams
Large organizations may have hundreds of applications using different technologies and development processes.
Maintaining consistent security requirements across such a diverse environment can be difficult.
Standardized frameworks, automation, shared tooling, and security champions can help address this challenge.
Balancing Security and Development Speed
Security can sometimes be viewed as a barrier to rapid software delivery.
A mature application security management program integrates security into existing workflows instead of relying entirely on manual approval gates.
Automated testing and risk-based exceptions can help teams maintain delivery speed while addressing important security concerns.
Managing Security Tool Noise
Multiple security tools can produce overlapping findings and false positives.
Without proper correlation and prioritization, developers may spend time investigating issues that have limited practical significance.
Application security posture management can help provide broader context by combining findings from multiple sources.
Talent and Skills Gaps
Application security requires knowledge of both cybersecurity and software development.
Organizations may therefore face difficulties finding professionals with sufficient expertise across application architecture, cloud platforms, secure coding, security testing, and risk management.
Application Security Manager and Application Security Monitoring
The abbreviation ASM can create confusion because it is also used for Application Security Monitoring.
Application Security Monitoring focuses on observing application behaviour and security events during runtime. It can provide visibility into how applications process requests, handle data, and respond to potentially malicious activity.
The application security manager, by contrast, is a role responsible for managing and coordinating the broader application security program.
The two concepts can work together. Runtime monitoring can provide valuable security information, while the application security manager can use that information as part of vulnerability management, risk assessment, incident response, and security governance.
The Evolving Role of the Application Security Manager
The role continues to expand as application environments become more interconnected.
Cloud-native development, APIs, artificial intelligence, low-code platforms, open-source software, and third-party services are changing how applications are designed and deployed.
As a result, application security managers are increasingly involved in architectural decisions, technology governance, software supply chain security, development processes, and enterprise risk discussions.
The role is moving beyond traditional vulnerability oversight toward broader responsibility for building secure and scalable software development practices.
Final Thoughts
An application security manager provides the leadership and structure needed to manage application security across development and production environments. The role connects technical security practices with governance, risk, and business requirements.
As application environments become more complex, effective application security management depends on visibility, consistent processes, risk-based prioritization, and close collaboration with engineering teams. Application security posture management supports that work by bringing security information together and providing broader context for decision-making.
A mature approach allows organizations to move beyond isolated security tests and manage application security as an ongoing part of software development and enterprise risk management.
Frequently Asked Questions
Q: What does an application security manager do?
A. An application security manager leads or coordinates application security strategy, testing, vulnerability management, risk assessment, governance, and collaboration with development teams.
Q: What is application security management?
A. Application security management is the broader process of protecting applications through secure development practices, testing, monitoring, vulnerability management, governance, and risk management.
Q: What is application security posture management?
A. Application security posture management provides a broader view of application security by bringing together information from security testing, runtime environments, dependencies, infrastructure, and other sources.
Q: What is application security risk management?
A. Application security risk management involves identifying, evaluating, prioritizing, treating, and monitoring risks that could affect applications and the business processes they support.
Q: What is ASM in application security?
A. ASM can refer to different concepts depending on context. In a job or organizational context, it can refer to an Application Security Manager. In technical security discussions, ASM can also mean Application Security Monitoring, which focuses on runtime visibility and detection.